Hacking Group in Gas Pipeline Attack Says It Shut Down, Blames U.S. ‘Pressure’
Experts have warned that the hacking group may simply be trying to take the heat off so they can regroup.
Getty
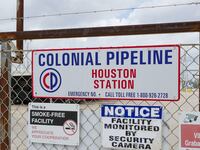
The hacking group accused of nearly crippling the U.S. gas supply on the East Coast with a ransomware attack on Colonial Pipeline says it is shutting down due to “pressure” from the U.S., according to The New York Times. “Due to the pressure from the U.S., the affiliate program is closed. Stay safe and good luck,” DarkSide said in a statement quoted by the Times on Friday. The Wall Street Journal first reported on the group apparently pulling the plug on operations. The group’s website has been down since Thursday. Experts have warned that the hackers’ announcement may simply be a way for the group to take the heat off themselves so they can reappear later, possibly under a different name. “I wouldn’t be surprised if DarkSide has just said, ‘It is way too hot,’ and they decided to pull the pin on themselves,” Winston Krone, the chief research officer with Kivu Consulting, Inc., told the Wall Street Journal. While President Biden on Thursday threatened to “disrupt [the ransomware group’s] ability to operate,” it was not clear if DarkSide was shut down by U.S. authorities.
Register below to read this article for free or subscribe
to unlock unlimited access to The Daily Beast.
Monthly
$1
First month then $5.99/month
Annual
$35
First year then $59.99/year
Premium
$79
First year then $119.99/year
*Substack access provided by the next business day, using your subscription email. Choosing the Premium plan constitutes your permission to share your subscription email with Substack and your agreement to Substack’s Privacy Policy.
Already have an account? Sign In
Looks like you already have a subscription!
- Account (completed)
- Payment (completed)
- Confirmation (completed)
You're all set!
Thanks for subscribing.
- 1Account
- 2Payment
- 3Confirmation